The Challenge
As the client’s business expanded, managing multiple cloud accounts, environments, and shared services became increasingly complex. The lack of standardized management led to inconsistent infrastructure, manual operational processes, and limited visibility into cloud costs.
Key problems included:
– Fragmented Cloud Accounts & Inconsistent Standards across environments and shared services
– Manual Operations & Scheduling that reduced operational efficiency
– High Operational Overhead & Limited Cost Visibility that made cloud resources harder to manage and optimize
The client needed a centralized yet flexible cloud management model to standardize infrastructure, automate routine operations, and improve cost efficiency without slowing down development.
The Solution
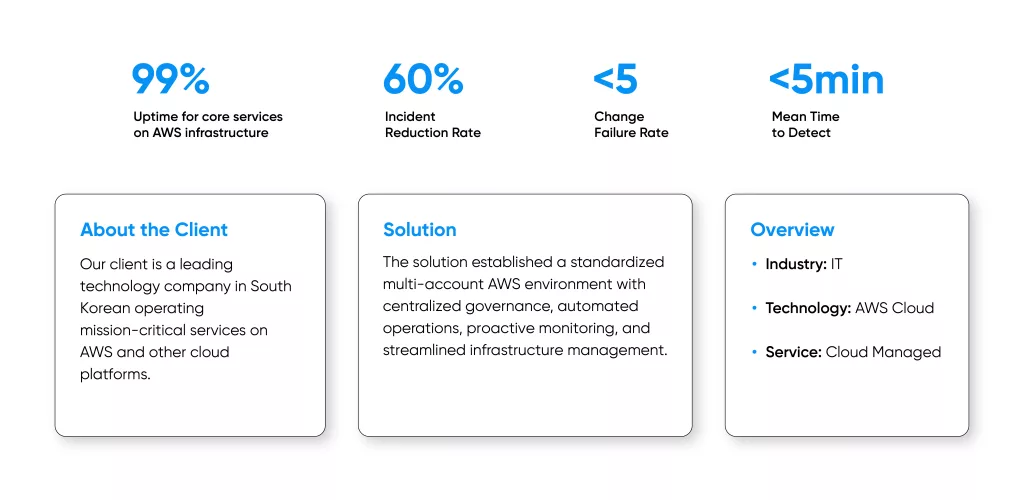
We helped the client establish and operate a standardized multi-account AWS environment built on AWS Control Tower. The solution centralized governance and shared services while preserving the flexibility of individual application environments.
Cloud Infrastructure Enablement
We designed and implemented a standardized multi-account landing zone with shared VPC and DNS patterns, Route 53 Private Hosted Zones, and Cloud Map-based service discovery.
Cross-account IAM roles and guardrails enabled centralized management of scheduling, monitoring, DNS, and security while allowing application teams to operate independently within their environments.
Proactive Operations & 24/7 Support
We integrated the cloud environment with the client’s existing monitoring stack, including CloudWatch, Datadog, and log analytics, and established clear incident and escalation processes.
Centralized health checks and alarms across EC2, RDS/Aurora, ECS/EKS, WAF, and CloudFront enabled faster issue detection and proactive response to potential service disruptions.
Automated Deployment & Continuous Improvement
We managed infrastructure changes, including IAM, VPC, Route 53, WAF, and scheduling, as code, with changes reviewed through pull requests and deployed systematically across development, staging, and production environments. This reduced manual effort and change risks while enabling the architecture to evolve with changing business requirements.
Security, Governance & Cost Optimization
We strengthened the client’s cloud security and governance through standardized IAM, DNS, and WAF configurations across accounts. The solution incorporated geo- and IP-based access controls at the CloudFront and Application Load Balancer layers, private service discovery through Route 53 and Cloud Map, and least-privilege S3 and IAM policies for internal services.
The Result
The solution delivered measurable improvements across key operational and business performance indicators.
- 99% Uptime for core services on AWS infrastructure
- 60% Incident Reduction Rate
- <5min Mean Time to Detect
<5% Change Failure Rate